
Last updated:
User Authentication
Dash0 supports multiple authentication mechanisms to balance ease of use with enterprise security requirements. You can sign in with a password, use social logins, or configure enterprise single sign-on (SSO) through SAML.
Password Authentication
You can register and sign in using your email address and a password.
Passwords must be at least 10 characters long and meet a minimum strength threshold based on zxcvbn, which evaluates resistance to common cracking techniques rather than relying on arbitrary complexity rules like requiring special characters.
Social Logins
Dash0 supports single sign-on through the following providers:
- GitHub: Sign in with your GitHub account.
- GitLab: Sign in with your GitLab.com account. Self-managed GitLab instances are not supported.
- Google: Sign in with your Google account.
A single Dash0 account can be linked to multiple authentication methods at the same time. For example, you can have password authentication, GitHub, GitLab, and Google all connected to one account. This means you never have to remember which method you used to sign up. Any linked method will get you into the same account.
Enterprise Single Sign-On (SAML)
For organizations that require centralized identity management, Dash0 supports enterprise SSO through SAML. Compatible identity providers include:
- Google Workspace
- Microsoft Entra ID
- Okta
- Any SAML-compliant identity provider
Dash0 enables self-service SSO per organization. Once it is enabled, you set up enterprise SSO yourself by configuring an enterprise connection for your organization. Contact support to request this.
Organization-Linked SAML Connections
A SAML connection can be linked to a specific Dash0 organization. When linked, any user whose email address matches the domain of the SAML connection is required to authenticate through that SAML connection before accessing the organization. The session must have been validated through the SAML provider, even if the user previously signed in with a password or social login.
Each email domain can be linked to at most one Dash0 organization. If your users need to sign in to multiple Dash0 organizations, use an unlinked SAML connection instead.
This enforcement applies only to the domain tied to the SAML connection. Users with email addresses on other domains can still be invited to the organization and authenticate normally.
Organization-linked connections provision users just in time. The first time a matching user signs in through the SAML connection, Dash0 adds them to the linked organization with the default role. No invitation is required, so you do not have to create accounts ahead of time. Removing such a user from the organization is not permanent on its own, because they rejoin on their next sign-in unless you also remove them in your identity provider.
Unlinked SAML Connections
It is also possible to establish a SAML connection that is not linked to an organization. In this case, users with a matching email domain are still verified through the SAML connection at sign-in, but they are not automatically added to any organization. Organization membership must be managed manually through invitations.
This is the recommended setup when users with the same email domain need access to multiple Dash0 organizations, since an organization-linked connection restricts the domain to a single organization.
Dash0 can also enable automatic invitations for an unlinked connection. Once enabled, a matching user receives an invitation to the mapped organizations the first time they sign in through SSO, and an unlinked connection can be mapped to more than one organization this way. Contact support@dash0.com to request this.
Team Sync from SCIM Groups
Dash0 can turn the groups in your identity provider into Dash0 teams and keep their membership in sync. You manage who belongs to which team in your identity provider, and the dataset access you grant to those teams follows automatically.
Prerequisites
- Enterprise connection: Your organization has an enterprise connection with both SSO and Directory Sync configured. You set up both yourself once Dash0 has enabled self-service SSO for your organization. Directory Sync is how your identity provider pushes users and groups to Dash0.
- Pushed groups: Every group you want in Dash0 is part of your identity provider's pushed-groups selection. Dash0 cannot see groups outside that selection.
- Admin role: You need the
Adminorganization role to turn team sync on or off.
Turn On Team Sync
-
Go to Settings → Teams. When your organization has an enterprise connection, the page shows This team list can be synchronized via SCIM.
-
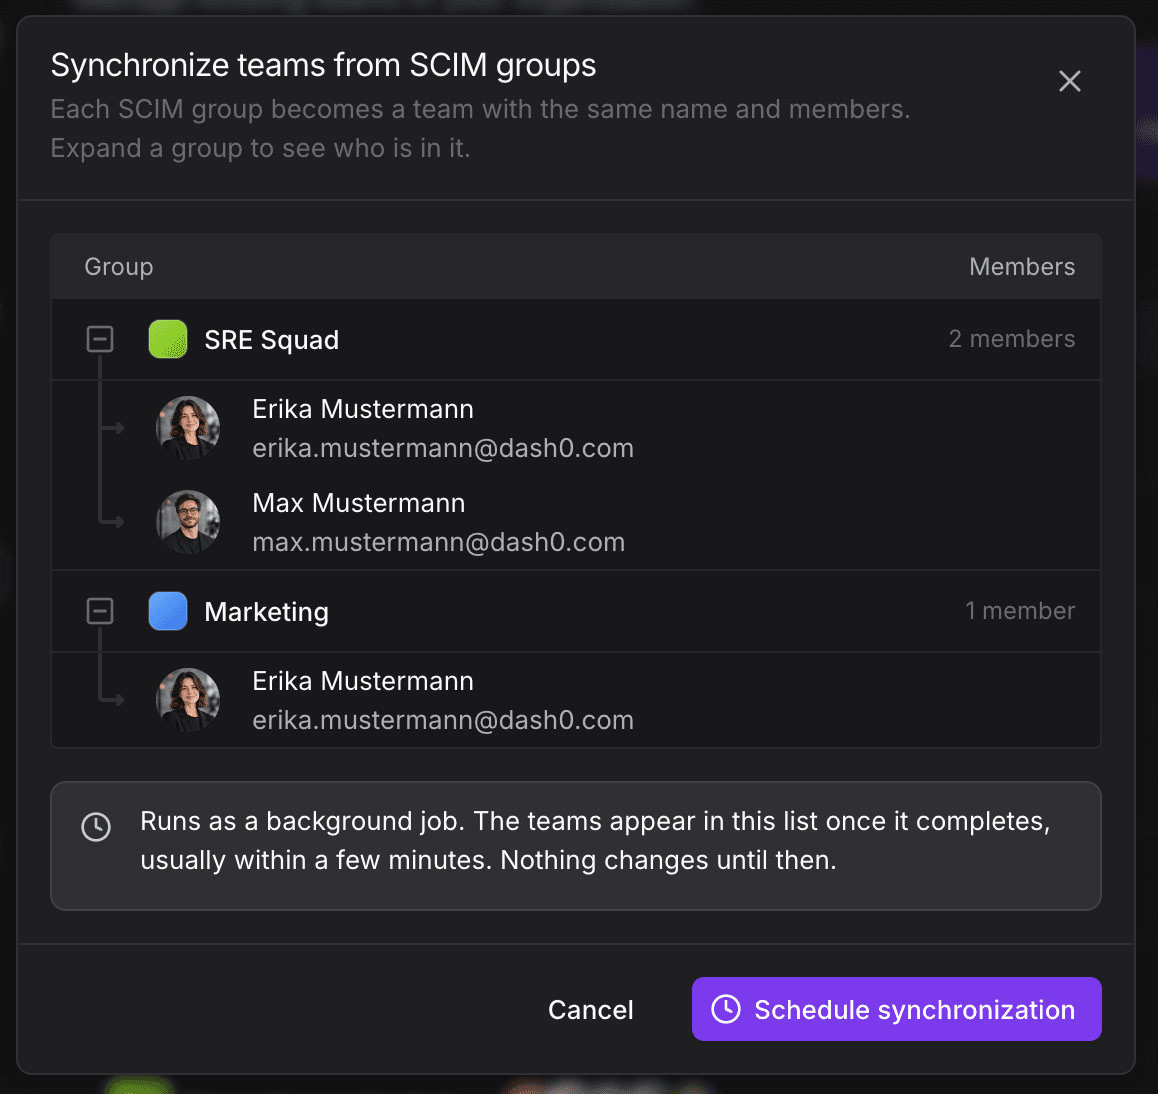
Click Review SCIM groups. The Synchronize teams from SCIM groups dialog lists each group and its members. Groups marked Name already in use have the same name as an existing Dash0 team. Dash0 creates a separate team for them and leaves the existing one alone.
-
Click Schedule synchronization. The synchronization runs as a background job and usually completes within a few minutes.
Reload the page after a couple of minutes. It then shows SCIM synchronization is on, and each synced team carries a Synced from SCIM badge. Click Sync now to run a pass on demand, or Disable synchronization to stop syncing.
How Synchronization Works
- Groups become teams: Each group becomes a team with the same name and members. A user in several groups joins several teams.
- Changes arrive when your identity provider pushes them: When a user joins or leaves a group, Dash0 updates their team membership once your identity provider pushes the change through Directory Sync. How quickly that happens depends on your identity provider's push schedule. This includes users provisioned through Directory Sync who have never signed in to Dash0.
- The identity provider wins: Membership of a synced team follows its group. A manual change to a synced team's members is reverted on the next sync, so make the change in your identity provider instead.
- Renames carry over: Dash0 matches a group to its team by the group's identifier, not its name. Renaming a group in your identity provider renames the existing team.
- Manual teams stay untouched: Teams created in Dash0 are never modified by the sync.
- Deprovisioning removes team membership only: When your identity provider deprovisions a user, Dash0 removes them from every synced team. Their organization membership is unchanged. Remove them from the organization in Settings → Members to revoke access.
- Removed groups leave empty teams: When a group is deleted or leaves the pushed-groups selection, Dash0 keeps its team but removes all members. The team keeps its dataset permissions. Delete the team in Dash0 if you no longer need it.
- Team membership only: The sync does not assign organization or dataset roles. Grant dataset access to the synced teams as you would to any other team.
Two-Factor Authentication
Dash0 supports two-factor authentication (2FA) using time-based one-time passwords (TOTP). You can set up 2FA with any compatible authenticator application, for example:
- Google Authenticator
- Authy
- 1Password
- Bitwarden
2FA is configured per user from your account settings. It is currently not possible to enforce 2FA at the organization level.
Session Lifetime
Sessions have a maximum lifetime of 31 days from the time of sign-in. After 31 days, you will be required to re-authenticate regardless of activity.